Cowrie Honeypot Analysis
I used Cowrie honeypot logs to examine the activity behind repeated login attempts, bringing event summaries and campaign-level observations into a pair of reports.
Academic security analysis. Python analysis, visualisation and report preparation.
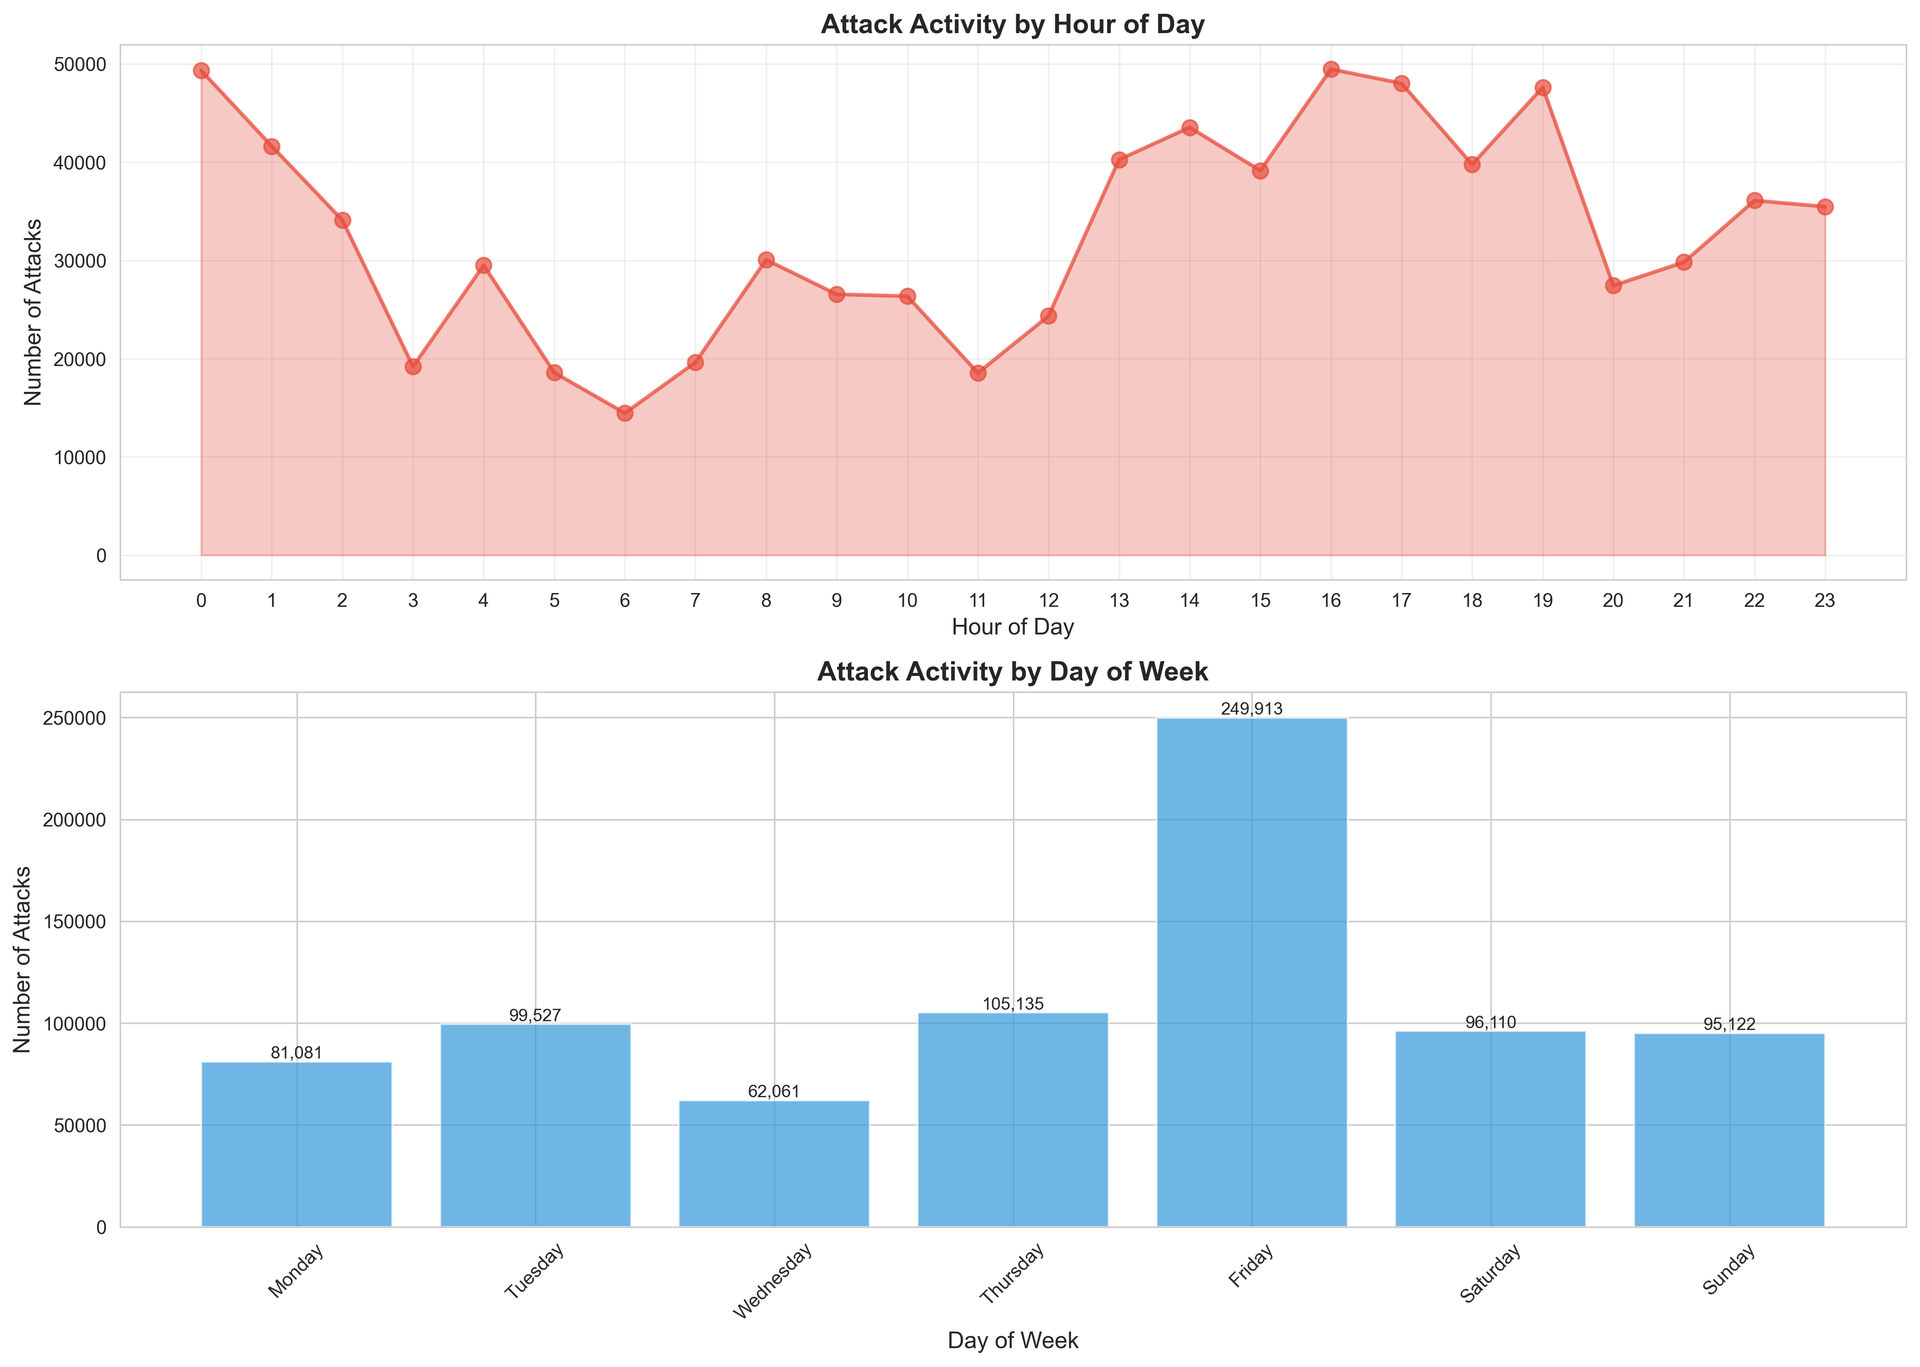
The starting point was a large collection of honeypot events, and I worked from those records towards views of authentication, session activity and the commands people attempted after gaining access, with the session records providing a way to connect separate events before interpreting their wider pattern.
The analysis code produced summaries and charts for timing, ports, credentials and command use, with separate query tools for looking more closely at the activity behind an aggregate count.
The saved report describes 480,998 events, and the repository preserves both an executive overview and a campaign deep dive, though those figures belong to that captured dataset and not an ongoing monitoring service.
The catalogue date follows the first preserved commit on 4 October 2025.
Outcome
A completed log-analysis workflow with charts and written reports. The public entry uses aggregate timing output rather than individual attacker addresses or credentials.